A recent cyberattack on European grocery store refrigeration systems has spotlighted the vulnerabilities in building automation systems, with hackers causing tens of millions of dollars in damages by tampering with temperature controls. This incident underscores the urgent need for U.S. facilities to address these security gaps before they become targets.
What Happened
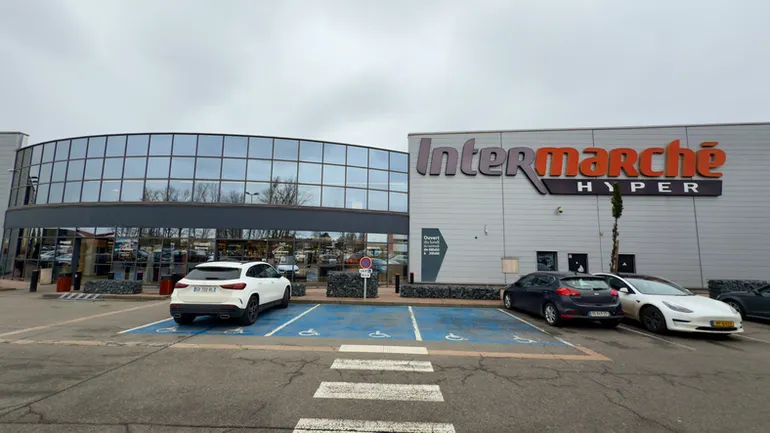
Hackers breached the refrigeration systems of European grocery chains, including Intermarché, on October 12, 2026. By manipulating the networked temperature controls, attackers were able to defrost refrigeration units, leading to massive losses of food products. This attack serves as a high-profile example of the risks associated with outdated building control systems, which often rely on legacy communication protocols that lack robust security features. Sean Tufts, field chief technology officer at Claroty, highlighted these vulnerabilities, warning that similar attacks could occur if systems are not upgraded or replaced. The breach has prompted security experts to call for immediate action to protect building systems from future cyber threats.
What This Means for Your Business
For U.S. operators in the construction, architecture, engineering, and manufacturing sectors, this incident is a stark reminder of the critical need for cybersecurity in building systems. Companies utilizing legacy systems are particularly at risk and should prioritize investments in modernizing their infrastructure to meet current security standards. Compliance with frameworks like the Cybersecurity Maturity Model Certification (CMMC) is essential, as is the implementation of Zero Trust architectures. These measures can help mitigate risks and protect against potential disruptions that could lead to significant financial losses and operational downtime.
What US Operators Should Watch
Decision-makers should closely monitor federal guidelines and deadlines related to cybersecurity compliance. Upcoming CMMC audit dates and procurement windows are crucial for ensuring that systems meet necessary security requirements. Additionally, operators should stay informed about potential funding opportunities for cybersecurity upgrades, which can offset the costs of necessary system enhancements. By staying proactive, U.S. companies can safeguard their operations against the growing threat of cyberattacks on building systems.
Source: Facilities Dive. Read the original story ->
Partner Insight · VisioneerIT
The increasing reliance on technology in construction makes cybersecurity a critical focus for companies aiming to protect their operations. VisioneerIT offers comprehensive services to help organizations achieve compliance and manage cyber risks effectively.
Explore VisioneerIT Cybersecurity →
Is your firm ready for what’s next?
VisioneerIT helps AECM and government contractors modernize operations, achieve compliance, and implement AI.
Explore VisioneerIT Solutions →