Hundreds of European supermarkets suffered significant financial losses when hackers infiltrated Danfoss refrigeration control systems, forcing units into defrost mode and causing tens of millions of dollars in food spoilage. This incident underscores the urgent need for U.S. facilities to address vulnerabilities in internet-connected building automation systems.
What Happened
The breach occurred on October 12, 2026, affecting supermarkets in countries including France, Spain, Portugal, Poland, Germany, and Belgium. Danish manufacturer Danfoss confirmed that their AK-SM800 and AK-SC355 refrigeration controllers were compromised, leading to temperatures rising to 122 degrees Fahrenheit. These systems, many of which are legacy products, no longer receive software or security updates. Danfoss has advised clients to update firmware and migrate to current-generation solutions, but the incident highlights the critical risk of outdated technology.
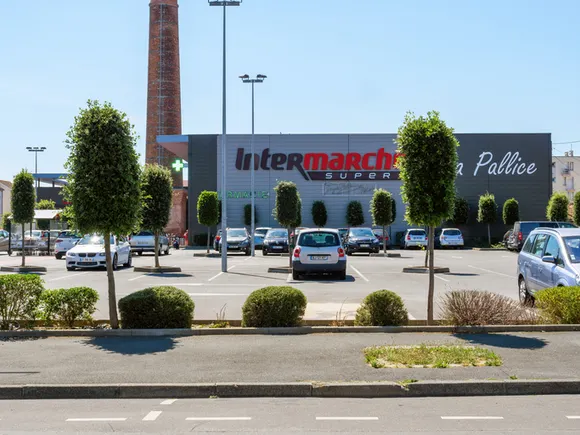
The attack exploited vulnerabilities in the Modbus communication protocol, a standard for building automation systems that lacks modern security measures. This breach is a stark reminder of the potential impacts of cybersecurity lapses on essential infrastructure, with Intermarché and other major grocery chains like Carrefour and Coopérative U bearing the brunt of the attack.
What This Means for Your Business
For U.S. companies, particularly those in the AECM sectors, this incident serves as a pressing reminder to reassess cybersecurity strategies and ensure compliance with standards like CMMC and NIST. The attack demonstrates the potential financial and operational risks associated with legacy systems and emphasizes the importance of adopting Zero Trust architectures to protect industrial control systems.
Businesses must consider the implications for procurement and contracts, ensuring that vendors and systems meet rigorous security requirements. Proactive measures, such as regular audits and updates, can prevent similar breaches and protect against significant financial losses. The incident also highlights opportunities for companies specializing in cybersecurity and system upgrades, as demand for secure, modern solutions is likely to increase.
What US Operators Should Watch
U.S. operators should monitor federal cybersecurity guidance and deadlines closely. The U.S. Cybersecurity and Infrastructure Security Agency has previously flagged vulnerabilities in systems like Danfoss's, and staying abreast of such advisories is crucial. Companies should prioritize compliance with upcoming CMMC audit dates and ensure that bid opportunities for federal contracts are aligned with robust cybersecurity measures. Continuous monitoring of procurement windows for system upgrades can also provide strategic advantages in maintaining secure operations.
Source: https://www.facilitiesdive.com/news/hack-of-danfoss-refrigeration-controllers-in-europe-causes-tens-of-millions/832832/. Read the original story ->
Partner Insight · VisioneerIT
The recent cybersecurity breach highlights the critical need for AECM companies to adopt comprehensive cybersecurity strategies and ensure compliance with standards like CMMC. VisioneerIT offers tailored solutions to help organizations protect their infrastructure and manage supply-chain cyber risks effectively.
Explore VisioneerIT Cybersecurity →
Is your firm ready for what’s next?
VisioneerIT helps AECM and government contractors modernize operations, achieve compliance, and implement AI.
Explore VisioneerIT Solutions →