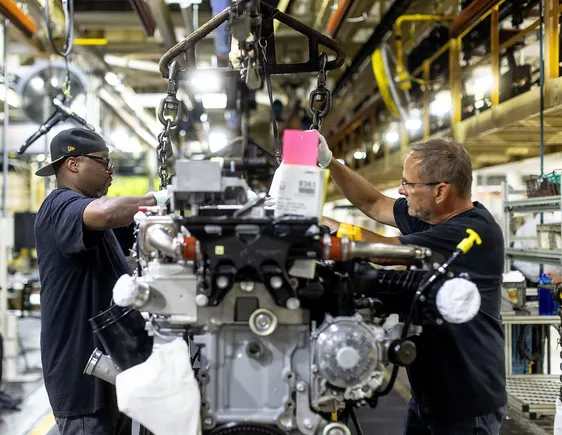
Manufacturers are making strides in patching software vulnerabilities, but identity management remains a critical cybersecurity weakness. This issue is particularly pressing as the sector continues to face sophisticated threats.
What Happened
Manufacturing Dive reports that the manufacturing sector is experiencing significant cybersecurity challenges, primarily due to inadequate identity management practices. According to a recent report by security firm Black Kite, approximately 70% of the largest manufacturers have had their credentials exposed on the dark web, a consequence of information-stealer malware. This vulnerability is compounded by the fact that about 75% of these firms are using software with at least one critical vulnerability, and 54% have vulnerabilities actively exploited by hackers.
Despite some progress in reducing critical vulnerabilities—down from 80% in 2024 to 75% in 2026—identity management failures persist. Misconfigurations remain a widespread issue, with 71% of ransomware victims in 2026 having failed to configure key technology components correctly. Additionally, over one-third of manufacturers have not properly configured their email anti-spoofing tools, leaving them and their partners vulnerable to phishing attacks.
What This Means for Your Business
For AECM professionals and government contractors, these findings underscore the importance of robust cybersecurity measures. Companies must prioritize identity and access management to protect their sensitive data and maintain trust with clients and partners. The persistent exposure of credentials on the dark web indicates a need for enhanced security protocols, such as multi-factor authentication and regular audits of access management systems. Moreover, the sector’s slow progress in addressing misconfigurations suggests an opportunity for firms to differentiate themselves by investing in comprehensive cybersecurity training and tools.
The financial implications are significant. Data breaches can lead to substantial fines, legal liabilities, and loss of business opportunities. Ensuring compliance with frameworks like the Cybersecurity Maturity Model Certification (CMMC) and adopting a Zero Trust approach can mitigate these risks and enhance competitive positioning.
What US Operators Should Watch
US manufacturers must keep an eye on evolving cybersecurity regulations and deadlines. Compliance with CMMC requirements is crucial, especially for those involved in government contracting. Firms should also monitor the release of new cybersecurity guidelines and updates from agencies like the Cybersecurity and Infrastructure Security Agency (CISA). Staying informed about the latest threats and mitigation strategies will be essential for maintaining operational security and competitive advantage.
Source: Manufacturing Dive. Read the original story ->
Is your firm ready for what’s next?
VisioneerIT helps AECM and government contractors modernize operations, achieve compliance, and implement AI.
Explore VisioneerIT Solutions →